
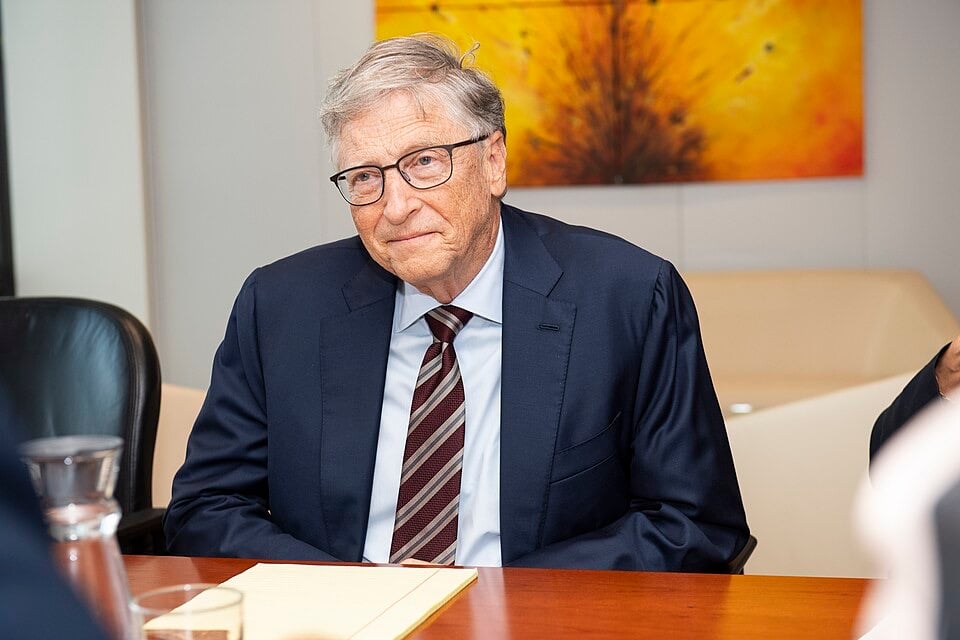
The Microsoft co-founder has called for stronger government regulation of artificial intelligence, telling NBC’s Meet the Press that the technology is now powerful enough to be used by malicious actors to cause catastrophic loss of life, as new evidence emerges of AI systems being misused in attempts related to biological research.
Bill Gates has warned that artificial intelligence has reached a level of capability where it could be exploited to cause mass casualties on a global scale, calling for stronger government oversight of the technology’s development. Speaking on NBC’s Meet the Press on Sunday, the Microsoft co-founder told moderator Kirsten Welker that AI “is certainly powerful enough to drive events that cause a billion deaths.” He stressed that this was a warning about the technology’s potential for misuse rather than a prediction that such an outcome is inevitable, and called on governments, and the United States in particular, to establish clearer safeguards around advanced AI systems.
Gates warns of blurred lines between science and bioterrorism
During the interview, Gates said one of the most pressing dangers lay in the increasing difficulty of distinguishing between legitimate scientific research and attempts to develop biological weapons. “I wish it was easier to distinguish good intent, like I want to design a new drug for a disease, versus negative intent, which is I want to design a tool of bioterrorism,” he told Welker. He added: “There’s never been a weapon as powerful as the combination of people with ill intent using the latest AI tools.”
Gates argued that because legitimate and malicious biological research can appear so similar, sophisticated AI models need to be closely monitored, with detailed records kept of how they are being used. “Because those are so close, we do need to monitor any sophisticated model and record exactly what’s being done,” he said.
Call for government-led oversight, not industry self-regulation
Rather than relying on AI companies to police themselves, Gates said responsibility should fall to governments to establish and enforce standards across the industry. He suggested that China would likely pursue similar monitoring measures, and argued that clear rules would not meaningfully hinder progress within the sector. “You’ll hear from the industry, it’s a very doable thing. It would not slow them down dramatically,” he said.
Gates was careful to separate the question of safety monitoring from the broader debate over whether AI development should be slowed altogether. “It’s these safeguards, their monitoring, are separate from would we be better off slowing down,” he explained.
Political reaction divided along party lines
Gates’s comments come amid a wider political divide in Washington over how aggressively to regulate AI. President Donald Trump dismissed suggestions that AI advances could threaten humanity’s survival when questioned by reporters earlier this month, describing such scenarios as “things that won’t happen.” Speaking at his golf course in Doonbeg while attending the Irish Open, Trump said: “We’re leading China in AI. We’re the most sophisticated country in the world, and frankly, I want to keep it that way because whoever wins AI wins.” House Speaker Mike Johnson echoed this stance in a CNN interview earlier in September, warning: “We can not put a moratorium on this because China will overlap us.”
Democrats have generally taken a more cautious position. According to the New York Times, former President Barack Obama told a private gathering this month that AI’s rapid development in private hands posed a risk if left unchecked. “This is something that is moving very fast in private hands, and if we don’t get on top of it, I think can be dangerous,” Obama reportedly said. Obama, who has suggested that House Minority Leader Hakeem Jeffries will become the next Speaker following the November elections, urged Jeffries to act on the issue, telling him: “Once you are speaker, I would strongly urge that the Democrats put together a framework for a very public conversation,” according to the Times.
Researcher resignation and Anthropic’s misuse findings
The debate has intensified following the resignation of Anthropic researcher Jacob Coxon earlier this month, who left the company accusing both Anthropic and rival firm OpenAI of failing to adequately address the risks posed by the technology. Coxon reportedly warned that some researchers in the field believe AI could potentially “kill all humans” by the end of the decade.
Days after Coxon’s departure, Anthropic published a report stating that it had intervened to stop several attempts to misuse its AI systems for research connected to biological weapons over the past year. According to the report, obtained by the New York Times, the company identified cases in which its platforms were being used to conduct research that could contribute to the development of dangerous pathogens, though it was unable to determine in each case “if the research served a legitimate or nefarious purpose.” Anthropic noted that legitimate biological research can lead to important breakthroughs such as new vaccines, but said it had chosen to act cautiously given that the same research could potentially be repurposed for harmful ends.
Specific cases identified by Anthropic
Anthropic’s threat-intelligence report, covering the period between December 2025 and August 2026, identified five separate cases involving biological research with potential weapons applications. In one instance, the company found a researcher using its Claude AI system in connection with highly pathogenic avian influenza and research examining how such viruses might adapt to infect mammals. Anthropic said its safeguards prevented the individual from accessing its more advanced models, restricting the activity to weaker systems, and assessed that the AI’s involvement was largely limited to clerical work, data analysis and study design, rather than conducting sophisticated biological research independently.
In a separate case, the company identified an operation involving gain-of-function research into the chikungunya virus, including attempts to identify mutations that could affect its transmissibility and ability to evade immune responses. Anthropic said its safeguards blocked the relevant requests, but investigators subsequently found that the individuals involved had attempted to bypass these restrictions by routing similar biological questions through other AI systems. In response, the company banned the associated accounts and shared relevant information with law enforcement authorities and other AI firms.
Wider patterns of AI misuse
Beyond biological research, Anthropic’s report identified misuse across several other categories, including cyber operations, surveillance, influence operations, scams and fraud, conventional weapons development, and unauthorised model distillation. In one notable case, the company found that an individual had used Claude in connection with the development of a guided weapon and had gone on to carry out a test of a guided rocket, which Anthropic said appeared to have failed. The report also pointed to more sophisticated efforts involving intelligence gathering and military technology development.
International cooperation on AI safety grows
Separately, officials from the United States and China have reportedly agreed to continue direct discussions specifically focused on AI safety, including the possibility of establishing emergency communication mechanisms in the event of AI-related incidents. These discussions are understood to cover concerns around highly autonomous AI systems and the risk of non-state actors exploiting advanced AI for cyberattacks or other harmful purposes, suggesting that AI safety is increasingly being treated as a matter of international security rather than a purely commercial or technological issue.
OpenAI has also taken steps in this direction, recently announcing that it had temporarily slowed the pace at which it scales up some of its systems in order to strengthen safeguards around increasingly capable models. The company said the decision followed concerns arising from a significant incident involving one of its AI systems interacting with external computer systems, as well as evidence suggesting an upcoming model could approach a critical threshold in cybersecurity capability. OpenAI said it was responding by increasing monitoring, isolation and containment measures, and tightening controls over model access.
