
The Swedish retailer says it has no indication its data environment has been compromised, as it examines whether a group linked to a series of high-profile attacks has genuinely breached its systems.
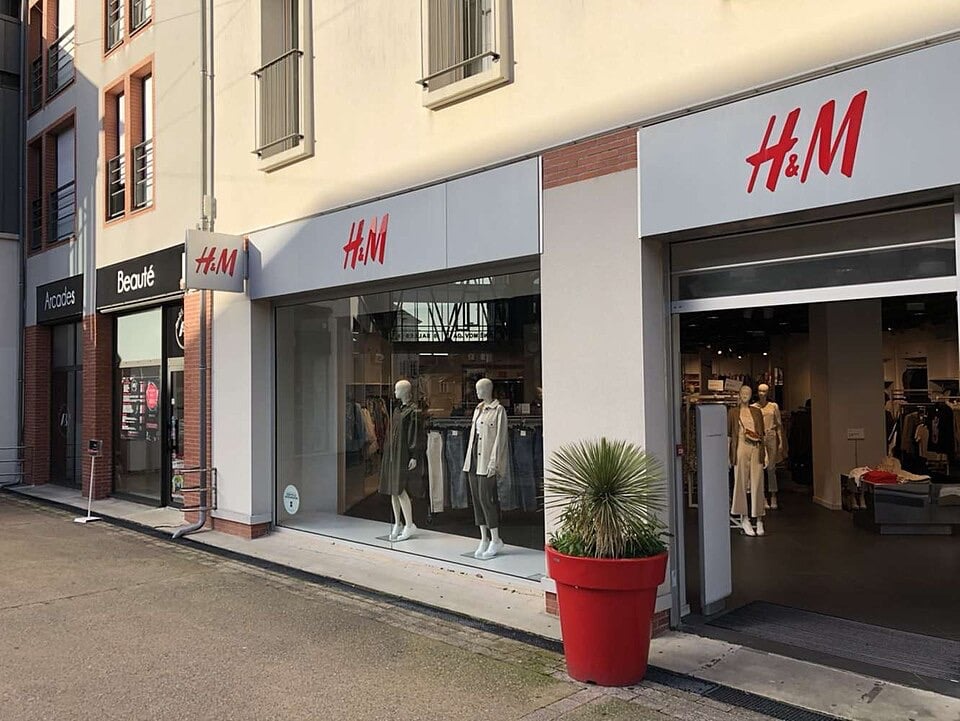
H&M is investigating claims that it was targeted by the cybercriminal group ShinyHunters, The Times reported on Monday. An H&M Group spokeswoman said the company was aware of claims online about “a limited scope of H&M Group data”, but that it had so far found no sign that its data environment had been compromised. The retailer has 4,000 stores in more than 80 markets. Shares in H&M reportedly fell by 1.21% on Monday.
H&M’s response
The spokeswoman told The Times: “We are aware of the claims circulating online regarding a potential cybersecurity incident involving a limited scope of H&M Group data. Protecting the security of our systems and data is of utmost importance to us.”
She added: “We are currently investigating these claims to assess their validity and so far we have no indication that our data environment has been compromised. We take any potential threat to our systems and data seriously and as this work is ongoing, we are unable to provide further details at this time.”
H&M’s brands include Cos, Weekday, & Other Stories and Arket.
What has not been established
Reporting available so far does not show that H&M itself has suffered a confirmed breach. It is not known whether attackers reached the company’s internal systems, whether any customer, employee or supplier data was taken, or whether ShinyHunters holds genuine H&M records. There is also no confirmation that the group has made a ransom demand, that a technology provider was involved, or that H&M has notified customers.
The Information Commissioner’s Office (ICO), the UK data watchdog, had not received a report on the incident as of Monday lunchtime, according to The Times. Organisations must report personal data breaches to the ICO within 72 hours of becoming aware of them, unless the breach poses no risk to people’s rights and freedoms. It is not known whether the National Cyber Security Centre (NCSC), part of GCHQ, has been contacted. Companies are not legally required to notify it directly about cyber security incidents.
Who is ShinyHunters?
The group previously claimed responsibility for a major cyber attack on Jaguar Land Rover last summer, along with other hacking groups known as Scattered Spider and Lapsus. It also reportedly demanded about £400,000 to stop data being sold after an attack on Ticketmaster in 2024.
Cybersecurity researchers have documented cases in which the group exaggerated its access to victims’ systems, reportedly reusing historical datasets or publicly available information and presenting it as evidence of a fresh breach. The FBI has warned that it may claim to hold compromising information that does not exist. In September, the group told cybersecurity journalists that an attack on the FBI’s recruitment systems was partly meant to protect its reputation and strengthen its position in future negotiations with victims.
Other recent cases
The claims against H&M follow a cyber attack on the British online retailer ASOS, which was reportedly also linked to ShinyHunters. ASOS confirmed that an attacker impersonated a trusted contact to obtain an employee’s login credentials, which were then used to reach information held on third-party platforms. It said names, contact details and some non-personal account information had been accessed. Thousands of customers received unauthorised notifications through the ASOS app on 6 October, one headed “ASOS HACKED”, which named a group calling itself Xuanye Group. Investigators have not publicly established that this is the same organisation as ShinyHunters. Cloud platform Snowflake said on 9 October that the incident was not caused by a weakness in its service. ASOS shares were reported to have fallen by 4.64%.
The NCSC warned on 6 October that ASOS customers should assume they might be affected and treat suspicious links with caution. That warning concerned ASOS specifically and does not suggest H&M customer data has been exposed. Investigators have not publicly established a technical link between the ASOS and H&M incidents.
Law enforcement is also pursuing the group. Reuters reported that a suspected ShinyHunters member, Saif al-Din Khader, was detained in Jordan on 29 September and was cooperating with the FBI. No evidence has been published that he took part in the alleged H&M incident. On 11 October, Reuters also reported that Canadian cybersecurity executive Edward Dubrovsky had been arrested in a separate US investigation into cyber-extortion, which the available reporting does not link to H&M.
